
Abacordo
Abacordo is the compliance platform I built after too many engagements ended with a beautiful spreadsheet that nobody updated. It holds your facts once, a server, a supplier, a risk, an incident, and lets ISO 27001, NIS2 and GDPR each ask their own questions of them. Your own AI assistant can work in it directly. You keep the judgement.
Built in Belgium, for Belgian frameworks, by someone who used to be the auditor. Currently in closed beta. abacordo.be
One set of records, three frameworks
Management systems drift apart quietly. The asset register says one thing, the risk assessment another, and the impact assessment was written before either. In Abacordo you record a fact once, and it is linked to everything that depends on it. Change a server, and the risk that names it, the control that treats it and the processing activity that runs on it all know. There is a real CMDB underneath, not a folder of documents about one.
What it covers
-
ISO/IEC 27001
Policies with a managed revision cycle, risk treatment, the Statement of Applicability and the Annex A controls, kept current as you work rather than assembled in the fortnight before the audit.
-
NIS2 in Belgium
Entity registration, coverage of the eleven risk-management measures, management body governance and training evidence, the CyberFundamentals self-assessment on the CCB maturity scale, and incident notification under the law of 26 April 2024, with the statutory deadlines in the system rather than in somebody's calendar.
-
GDPR
Records of processing, impact assessments, article 32 measures and breach notifications, linked to the same assets and controls that already protect the data they describe. Your DPO and your CISO stop maintaining two truths.
-
Incidents with two sets of clocks
One break-in can be a significant NIS2 incident and a personal data breach at the same moment. Abacordo runs the 24-hour, 72-hour and one-month NIS2 clocks and the 72-hour GDPR clock from the one record, and shows what the incident still owes.
-
Your risk method, not mine
Qualitative, semi-quantitative or quantitative, your own scales and matrix. A new organisation starts on ISO 27005 scales and changes them afterwards.
-
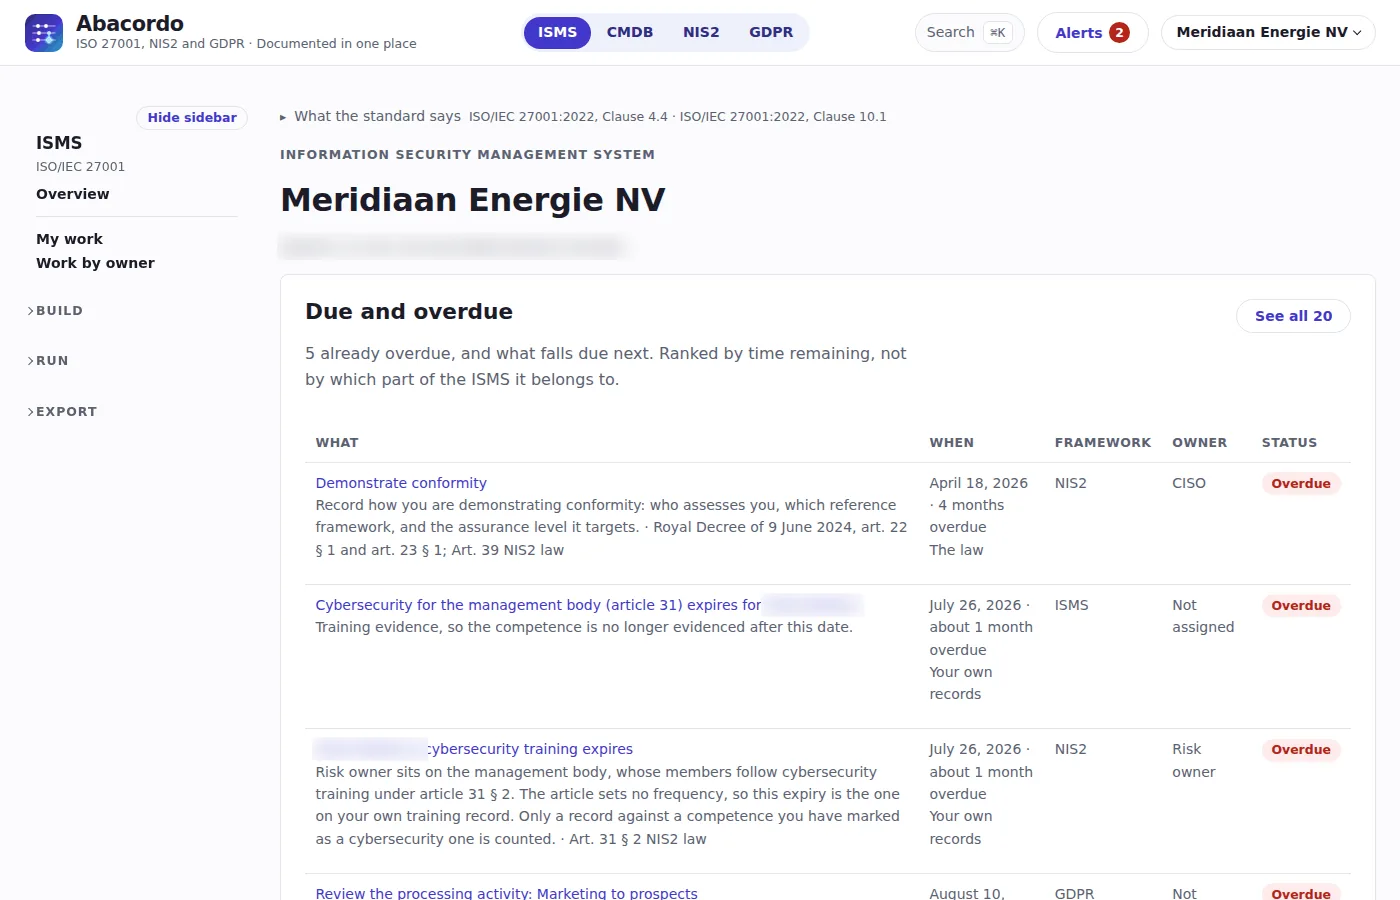
Calendar and readiness
Everything that expires or falls due, across all three frameworks, in one list, plus a readiness score by area so you can tell the board where you are.
-
Evidence and audit trail
Every change to every record is attributed. An auditor reads the history, not a summary of it, and the whole management system exports as one package.
-
Modules you can switch off
NIS2 and GDPR are modules. An organisation that only needs ISO 27001 never sees them.
Your own AI, inside your management system
Every organisation gets its own address for the Model Context Protocol. Add it to Claude, ChatGPT or whichever assistant you already use, approve the connection once, and it can work in the register directly: find the assets with no owner, draft an access-control policy from the controls you already have and link it to them, or check whether an incident is significant under NIS2 and what it still owes.
It documents; it does not decide. The assistant works under the connecting member's own role, cannot reach a module you have switched off, and every write lands in the activity log under that member's name. Abacordo holds none of your API keys and makes no model choice for you.
How you can use it
- As part of an engagement. I set it up during a gap analysis or an ISO 27001 implementation and hand you a register that is already populated.
- On your own. Request access to the closed beta. I take on a small number of organisations at a time so each one is set up properly.
- As a consultant or a group. Run several organisations in separate tenants with strict separation.
Reads in English, Dutch and French.
Want to see it against your own frameworks? Book a 30-minute demo. Bring your current register, spreadsheet or not, and I will show you what it looks like in Abacordo. Book a demo → or request beta access →